

Alert Fatigue: Why More Security Tools Doesn’t Mean Better Security
Updated on 06.05.2026
In the boardroom of many UK businesses, there is a lingering misconception that security is a “purchase.” The logic is simple: if we buy more tools, more firewalls, more endpoint protection, more identity monitors, we must be safer.
This “tool sprawl” has led to an era of unprecedented digital noise, giving birth to one of the most dangerous phenomena in modern cybersecurity: Alert Fatigue.
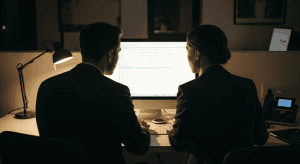
At Opticore IT, we often speak with IT managers who feel like they are standing under a waterfall of data, trying to catch the one “important” drop in a bucket.
When your security dashboard is permanently flashing red with 5,000 alerts a day, the human brain eventually does the unthinkable: it stops looking.
What is Security Alert Fatigue?
Security Alert Fatigue occurs when IT and security teams become overwhelmed by the sheer volume of security notifications generated by their various monitoring systems. It is the digital equivalent of the “boy who cried wolf.”
When a system sends 100 alerts an hour, and 99 of them are “False Positives” (benign events misidentified as threats), the one genuine “True Positive” is often missed. The consequences are catastrophic.
High-profile breaches, such as the infamous Target or Equifax hacks, weren’t caused by a lack of tools; they were caused by alerts being generated, but ignored or buried under a mountain of irrelevance.
The Psychological Impact:
- Burnout: Security professionals are in high demand and short supply. Asking them to manually sift through “noise” leads to rapid turnover.
- Apathy: Over time, the instinct to investigate every lead is replaced by a “check-the-box” mentality.
- Decision Paralysis: Faced with too much data, teams often struggle to prioritise which threat to neutralise first.
The SIEM Paradox: Logs, Logs everywhere, but Not a Threat to See
To solve the data problem, many firms implement a SIEM (Security Information and Event Management) system. A SIEM acts as a central aggregator, pulling in logs from your firewalls, servers, and cloud applications.
In theory, the SIEM is the “brain” of your security. In practice, without expert tuning, it becomes a megaphone for every minor hiccup in your network.
The Challenges of SIEM Log Analysis:
- Volume vs. Velocity: A mid-sized UK firm can generate millions of log entries per day. Processing this in real-time requires immense computing power and human oversight.
- Context Deficit: A log entry might show a “failed login attempt.” On its own, that’s noise. But if that failed login is followed by a successful login from a different IP address in a different country, that’s an incident. Connecting those dots is the hard part.
- The “Default Settings” Trap: Many tools come with out-of-the-box alerting. Without customising these to your specific business logic, you will be alerted every time a developer runs a legitimate test or a user forgets their password.
Enter the SOC: The Filter Between “Noise” and “Reality”
This is where a Security Operations Centre (SOC) becomes the essential layer of your defence. A SOC isn’t just a room full of screens; it is a combination of human intelligence and advanced automation designed to perform Triage.
A SOC’s primary job is to filter out the “False Positives” so that your internal team only sees the “Actionable Intelligence.”
How a SOC Filters the Noise:
- Tier 1 Analysis (The Sifters): Automated tools and junior analysts filter out the 90% of alerts that are known false positives or low-risk events (e.g., a known user on a bank holiday working from a hotel).
- Correlation: The SOC looks for patterns across multiple tools. They link a “suspicious file download” on an endpoint with an “unusual outbound connection” on the firewall.
- Threat Hunting: Instead of waiting for an alert, SOC analysts proactively search your logs for “Indicators of Compromise” (IoCs) that automated tools might have missed.
Why 24/7 Matters for UK Firms:
With the rise of global supply chains, a threat might originate from a server in Asia while your London office is asleep. If a breach is detected and stopped at 3:00 AM, the business opens on Monday as usual. If it is detected on Monday morning, the business might be offline for a week.
Incident Response Best Practices: Beyond the Alert
If an alert turns out to be a real threat, how you respond in the first 60 minutes defines your recovery cost. Here are the best practices we implement at Opticore IT:
- Immediate Isolation: Don’t just “delete” the malware. Isolate the affected machine from the network to prevent lateral movement.
- Root Cause Analysis: Finding the virus is easy; finding how it got in (the “Ingress Point”) is hard. If you don’t close the hole, they will be back tomorrow.
- Preserve Evidence: For insurance and legal reasons (GDPR), you must document the timeline of the breach and what data was accessed.
- Defined Escalation Paths: Everyone should know exactly who to call at 4:00 AM. If the “Incident Response Plan” is a dusty PDF no one has read, it’s useless.
Moving from “More Tools” to “Better Outcomes”
In 2026, the competitive advantage for UK businesses isn’t having the most security tools—it’s having the most efficient security operations.
Adding another blinking light to your server room won’t make you safer if no one is watching it. In fact, it might make you less safe by adding to the noise that hides the real danger.
The Opticore IT Approach
At Opticore IT, we don’t just sell you software. We provide the “eyes and ears” your business needs. Our managed SOC services are designed to:
- Silence the Noise: We tune your SIEM and tools so that you aren’t bothered by trivialities.
- Eliminate Blind Spots: We ensure your logs are talking to each other across your entire infrastructure.
- Provide Peace of Mind: You sleep; we watch.
Conclusion: Quality Over Quantity
The era of “collecting” security tools is over. We are now in the era of Security Orchestration. If your team is feeling the weight of alert fatigue, it is a sign that your architecture is broken, regardless of how much you spent on it.
By leveraging a professional SOC and focusing on high-fidelity monitoring, you can turn your security from a source of stress into a silent, reliable engine of business continuity.
Other Articles You May Like...
The latest blogs from Opticore
View All Blog Articles
28.10.2026
Ekahau, Sidekick and Spectrum Analysis: The Tools Behind a Professional WiFi Survey
28.10.2026
Network Documentation: Why Auditors, Insurers and Acquirers All Ask for It
28.10.2026
What to Look for in a Wireless Survey Report: Heatmaps, Findings and Red Flags
28.10.2026
Ekahau, Sidekick and Spectrum Analysis: The Tools Behind a Professional WiFi Survey
Read Article28.10.2026
What to Look for in a Wireless Survey Report: Heatmaps, Findings and Red Flags
Read Article
28.10.2026