Network Audit Services

Uncover hidden risks, optimise performance, and improve compliance with a thorough, expert-led network audit. Industry-proven methodologies. Trusted by leading UK enterprises.
Book a Discovery Call

Trusted by 250+ customers worldwide

Bright colorful blogging logo for social media, digital marketing or online branding.Fresh veggie burger with lettuce, tomato, and cheese on a bun.NatWest bank logo with red and purple colors.Cozy moon and stars logo for Premier Inn hotel chain.Vibrant colorful SKY logo with gradient effect and modern design.A close-up of a white bread loaf on a wooden cutting board.Close Brothers logo with company name in blue text and circular emblem.Fidelity Investments logo with gold and white icon and green text.Fidelis logo with black text on green background.Modern laboratory equipment for scientific research.Person lifting weights in gym.Lloyd's of London logo on a black background.A Flutter logo with a gradient blue icon and grey text. Bright colorful blogging logo for social media, digital marketing or online branding.Fresh veggie burger with lettuce, tomato, and cheese on a bun.NatWest bank logo with red and purple colors.Cozy moon and stars logo for Premier Inn hotel chain.Vibrant colorful SKY logo with gradient effect and modern design.A close-up of a white bread loaf on a wooden cutting board.Close Brothers logo with company name in blue text and circular emblem.Fidelity Investments logo with gold and white icon and green text.Fidelis logo with black text on green background.Modern laboratory equipment for scientific research.Person lifting weights in gym.Lloyd's of London logo on a black background.A Flutter logo with a gradient blue icon and grey text.
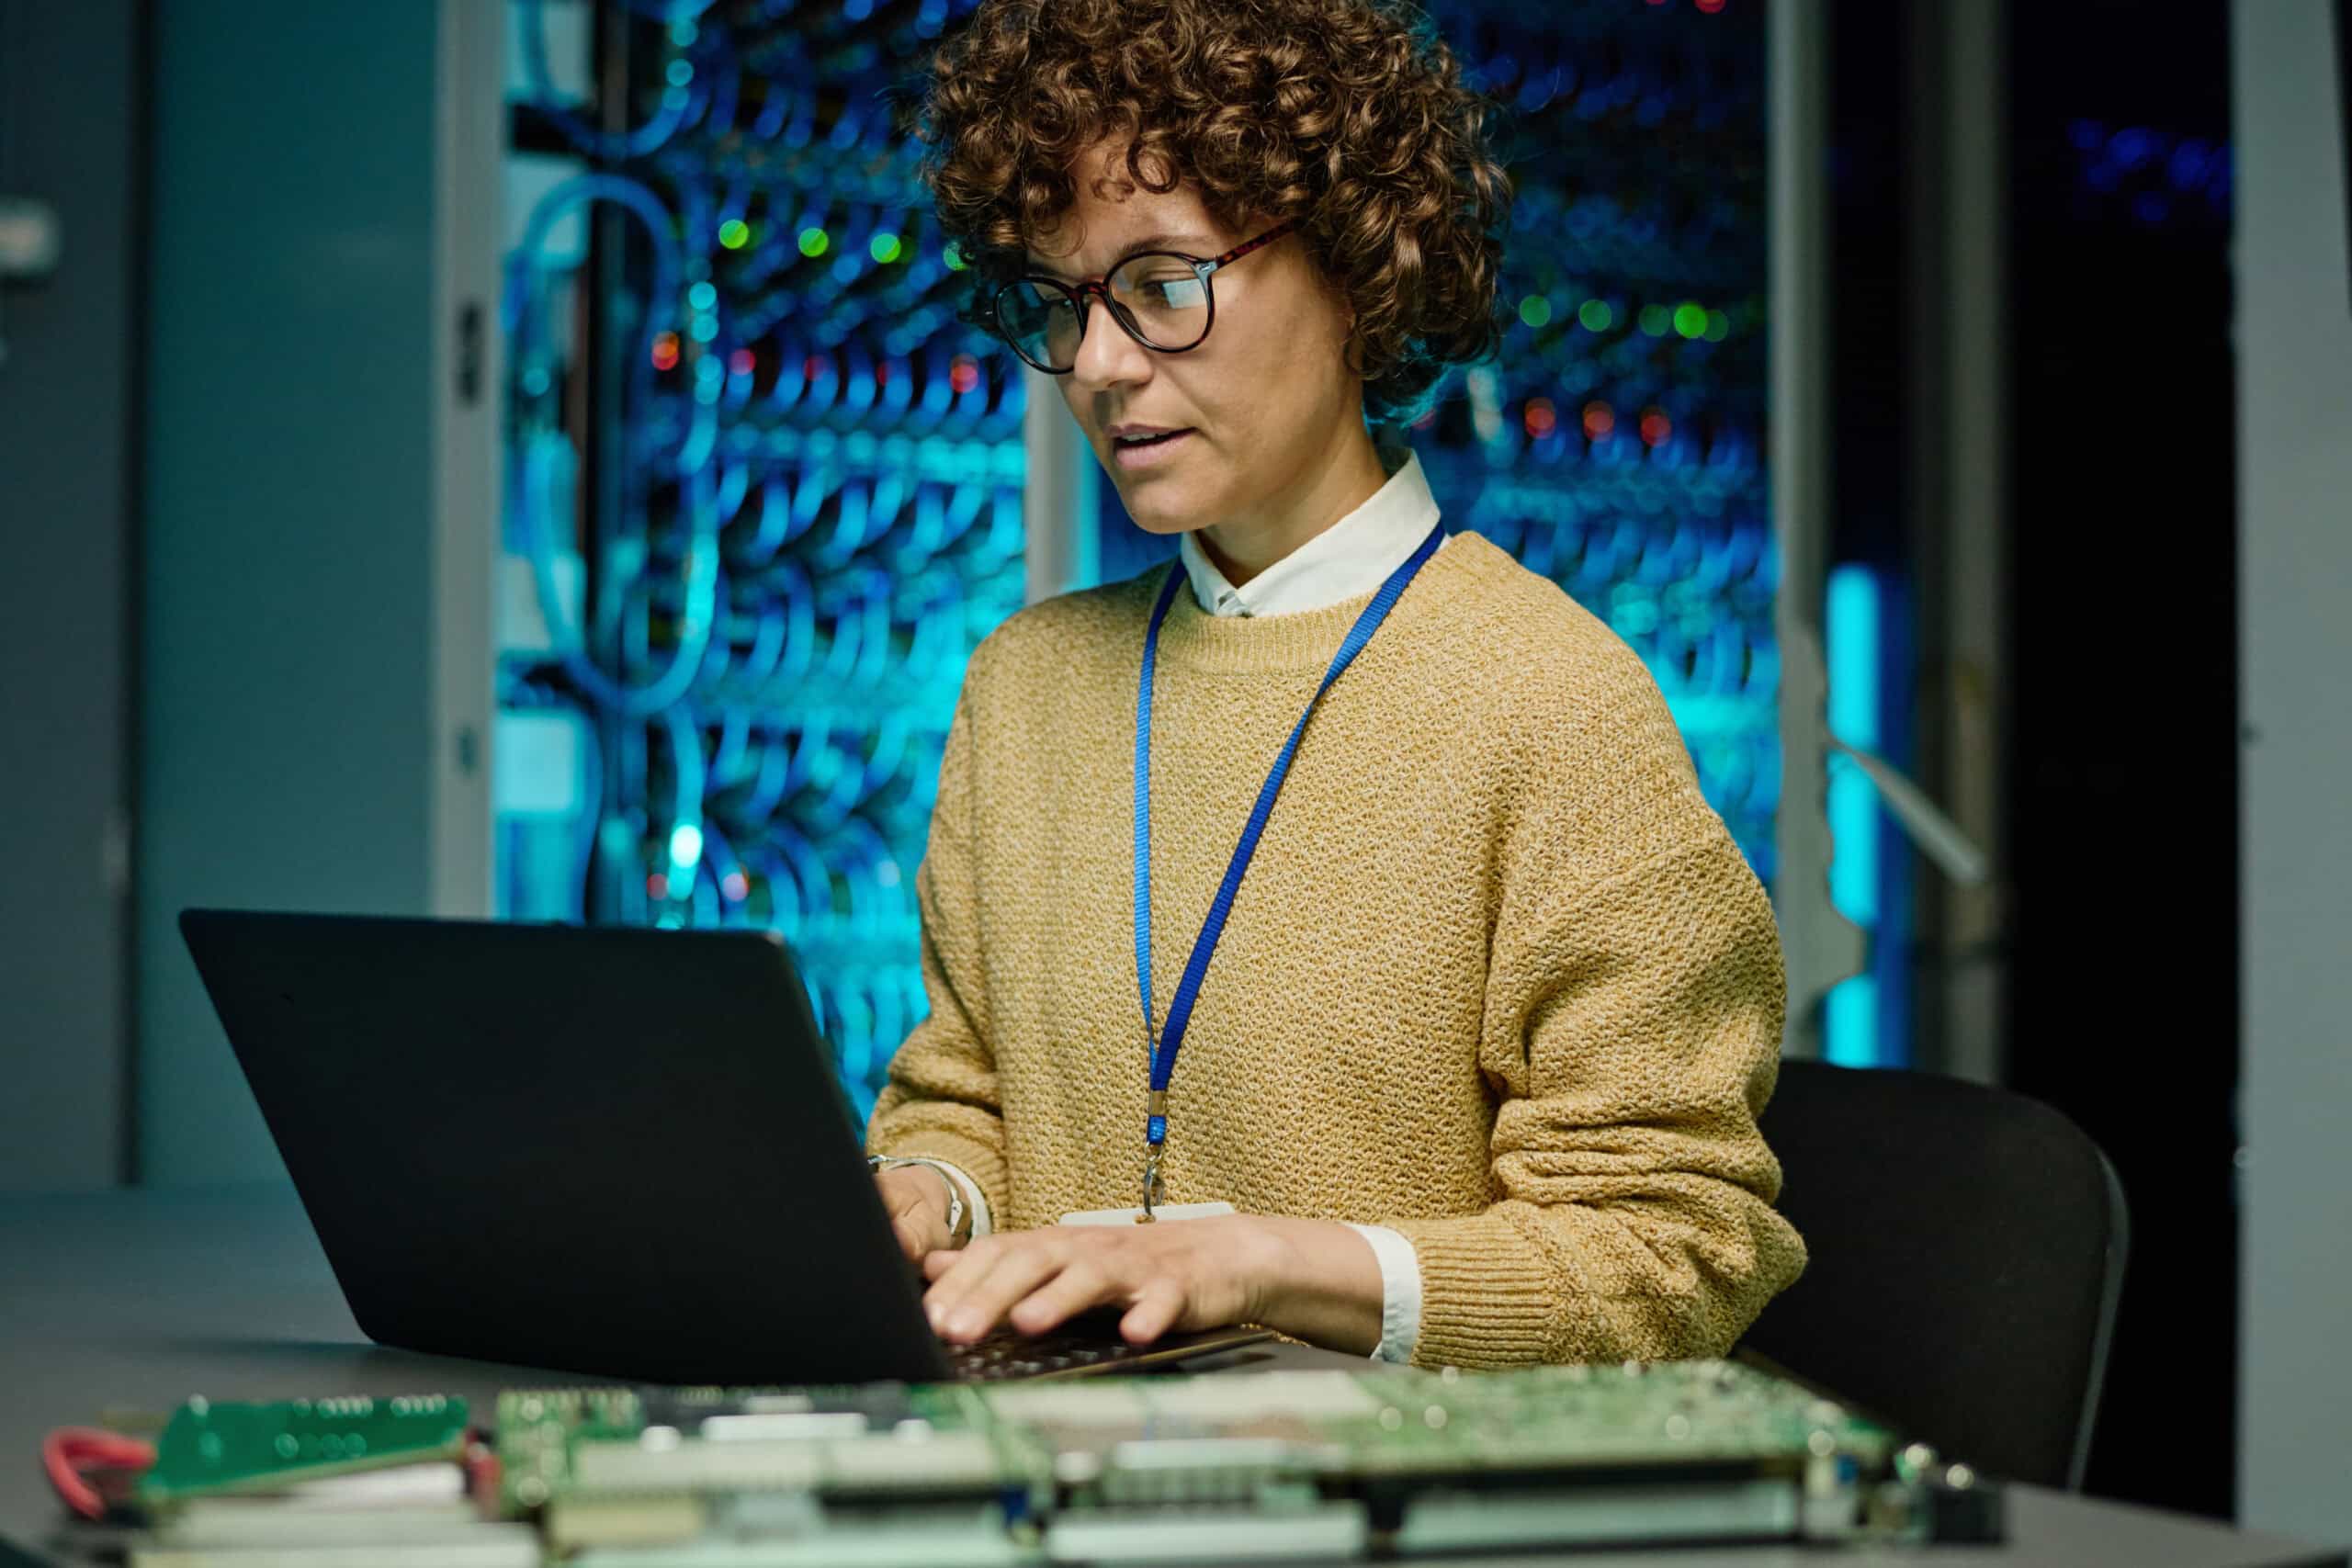
Female technician working inside a server room with network cables and equipment.

Uncover Hidden Risks in Your IT Infrastructure

Our network audits are independent, led by senior engineers, and trusted by some of the UK’s most demanding enterprises. We are ISO 27001 certified, and we have done this enough times to know where the problems usually hide.

Most businesses only look closely at their network when something has already gone wrong. The rest of the time it just runs, quietly carrying everything else, until an outage, a breach, or a failed audit forces the issue. By then, the warning signs have often been there for years, sitting out of sight because no one had the full picture.

A network audit gives you that picture. Maybe your network has grown piece by piece, maybe it has been through a lot of change in a short time, or maybe no one has properly looked at it in years. Whatever the reason, our UK-based engineers go in deep and come back with the facts: what is working, what is not, and what actually needs your attention. And because every audit is also a full security assessment, we tend to find the risks while they are still cheap to fix.

Server technician working on network hardware in a data center.

What is a Network Audit?

A network audit is a structured, independent assessment of your IT infrastructure across four dimensions: performance, design, security, and compliance. It examines the architecture, configuration, and live behaviour of your network using a combination of automated discovery tools and hands-on expert analysis.

An audit reveals inefficiencies, outdated and end-of-life hardware, security vulnerabilities, and misconfigurations across wired, wireless, data centre, and cloud-connected environments. The output is a detailed network audit report with prioritised remediation actions, so you can strengthen your network and align it with your business needs and industry best practices.

A network audit goes considerably deeper than a standard network health check. A health check gives you a snapshot of your current status. A full audit analyses security posture, configuration quality, performance under load, and compliance alignment, then sets out a strategic plan to fix what it finds.

Uncover the Unknowns in Your Network

Identify weaknesses early and address them before they become costly problems.
Request Your Network Risk Assessment

What Our Network Audit Services Include

Full Network Discovery

Mapping of physical and logical topology from Layer 1 to Layer 4 using automated discovery and on-premise scanning, giving you an accurate, current inventory of every device.

Security & Compliance Review

A network security audit that identifies vulnerabilities and misconfigurations and aligns your environment with the frameworks that matter to UK businesses, including ISO 27001, Cyber Essentials and Cyber Essentials Plus, PCI DSS, UK GDPR, and FCA operational resilience.

Performance Analysis

Traffic and throughput evaluation to pinpoint bottlenecks, troubleshoot slow network issues, and improve the experience for users and applications.

Configuration & Device Review

Assessment of switches, routers, firewalls, and wireless controllers for end-of-life risk, configuration drift, and vendor-specific weaknesses.

Remediation Planning

Prioritised recommendations ranked by severity and business impact, from quick wins to critical issues that need immediate attention.

Stakeholder Workshop

A presentation of findings and strategic next steps, with the option of ongoing support and remediation from our engineering team.

Data center technician with a tablet working on server racks.

The industries we audit

We deliver network audits for organisations where uptime, security, and compliance are non-negotiable. Our engineers understand the regulatory and operational pressures specific to each sector.

• Financial services and banking. Merchant banks, asset managers, and insurers operating under FCA expectations and strict data protection requirements.
• Legal and professional services. Firms handling sensitive client data where confidentiality and resilience are critical.
• Retail, hospitality, and leisure. Multi-site estates that depend on reliable connectivity across many locations.
• Media and broadcast. High-bandwidth, low-latency environments where performance directly affects output.
• Commercial real estate and building management. Networks underpinning smart buildings and shared tenant infrastructure.
• Public sector and not-for-profit. Organisations balancing tight budgets with compliance obligations.

If your sector is not listed, our methodology adapts to any environment, from single-site offices to complex multi-site WANs and hybrid cloud estates.

Hand connecting cables to a server in a data center.

Compliance, mapped to your sector

Compliance rarely fails at the level of policy. It fails in the infrastructure: the unpatched firewall, the flat network, the forgotten admin account. Because our audit examines exactly those layers, it gives you evidence against the standards your sector is actually held to, rather than a generic checklist.

  • Financial services firms see findings framed around FCA operational resilience, and where you run EU subsidiaries or serve EU clients, we align the assessment with DORA.
  • If you take card payments, whether in retail, hospitality or finance, we measure your network against PCI DSS so that cardholder data is properly segmented and protected.
  • When you are bidding for public sector or enterprise contracts, where Cyber Essentials or Cyber Essentials Plus is often a condition of entry, we show you precisely what stands between you and certification.
  • Wherever you hold personal data, we assess your environment against UK GDPR and the Data Protection Act 2018.
  • And for teams working towards ISO 27001, the audit doubles as a readiness check on the technical controls at the heart of the standard.

This will give you is a precise picture of where you stand against each requirement and a prioritised plan to close the gaps, which makes the assessment that follows faster, less costly, and far less stressful.

The tools and methodology behind every audit

A reliable audit combines automation for breadth with engineering judgement for depth. We use enterprise-grade automated discovery to map your estate quickly and accurately, vulnerability scanning to surface security weaknesses, and configuration analysis to detect drift and end-of-life risk. Our engineers then validate and interpret that data, because raw tool output is not an audit on its own.
 
Findings are consolidated, monitored, and reported through our bespoke OHMP platform, giving you a single, clear view of network health, risk, and the priorities that matter most.
 
We are vendor-agnostic. We assess what you have on its merits rather than steering you toward a particular manufacturer, so the recommendations you receive serve your business, not a hardware sales target.

Scoping and discovery call.

Before we touch anything, we sit down with you to agree on what the audit needs to achieve, the objectives that matter most, and any compliance drivers shaping the work. No two networks are alike, so the plan is built around yours from the very first conversation.

Automated discovery

Using enterprise-grade tooling and on-premise scanning, we build an accurate, current inventory of every device and map your topology from Layer 1 to Layer 4, giving us a complete picture before any judgment is made.

Analysis and validation

Our engineers interpret what the tools surface, examining configurations, traffic, security posture, and compliance alignment, then validate every finding by hand. Raw scan data is full of false positives, and removing them is what separates an audit from a report dump.

Risk scoring

We score each finding by severity and business impact, so you can see at a glance what demands attention today and what can safely wait, without wading through technical noise.

Reporting

You receive a comprehensive network audit report: prioritised recommendations, clear risk scores, and a remediation roadmap written to be understood by your board as well as your IT team.

Stakeholder workshop

We talk you through the findings in person, explain what they mean for the business, and agree the next steps together rather than leaving you with a document and no direction.

Optional remediation

If you would like us to, our engineers can implement the fixes and design the improvements. The choice is entirely yours, and there is no obligation to use us for the work we recommend.

Female technician working on a laptop in a server room.

Why get a network audit from Opticore

UK-based expertise, global standards. Headquartered in London with engineers deployed nationwide, we understand the realities facing British businesses, from FCA scrutiny in the City to the operational pressures on multi-site retail and public sector estates.

Independent and vendor-agnostic. We do not resell hardware, and we are not tied to any manufacturer, so our recommendations are built around your risk profile, your objectives, and your budget, never around a sales target. When we tell you something needs replacing, it is because the evidence says so, and that independence is precisely what makes an audit worth commissioning.

Nationwide emergency response. When something breaks, speed matters. Our Rapid Engineer Deployment Team is on standby for critical troubleshooting, active security threats, and outages, ready to mobilise across the UK so a problem on your network does not become a problem for your business.

24/7/365 managed services. An audit is a moment in time, but networks change every day. Through our bespoke OHMP platform we deliver continuous monitoring, analytics, and management, giving you a single, clear view of network health and the assurance that issues are caught as they emerge rather than at your next review.

Transparent partnership. No jargon, no black boxes, and no surprises. We keep you informed at every stage, so you always understand your security status, the priorities in front of you, and the value being delivered.

Network Audit for a Leading Merchant Bank

Problem

Our client, a top-tier UK financial institution, needed a full network assessment before embarking on a transformation programme.
Young man wearing headphones at office, using a stylus on a computer screen.

Plan

Our team conducted automated discovery, validated data, and produced a comprehensive audit. Findings included multiple critical vulnerabilities, EOL equipment, and misaligned security configurations.
Man working at computer with headphones in office environment.

Result

The client used our prioritised remediation plan to mitigate risk and confidently move forward with strategic network redesign.
High-tech cryptocurrency mining rig with multiple graphics cards and blue USB connections.
Young man wearing headphones at office, using a stylus on a computer screen.
Man working at computer with headphones in office environment.
High-tech cryptocurrency mining rig with multiple graphics cards and blue USB connections.

Network Audit FAQs

Will an audit disrupt my operations?

No. Our discovery and scanning techniques are non-invasive and conducted in coordination with your team to minimise impact.

How much does a network audit cost in the UK?

Cost depends on the size and complexity of your estate: the number of sites, devices, and the depth of compliance review required. We scope every audit individually and provide a fixed quote after a short discovery call, so there are no surprises. Audits are priced on scope rather than a flat rate, and we are happy to talk through the variables with you.

How long does a network audit take?

Most audits run from scoping to final report within two to four weeks, depending on the size of the environment. Automated discovery is fast; the time is spent on validation, analysis, and producing a report you can act on.

Do you carry out audits remotely or on-site?

Both. Much of the discovery and analysis can be done remotely, with on-site work arranged where physical inspection, cabling, or data centre review is needed. We agree the approach with you during scoping.

Will the audit access or expose our sensitive data?

Our discovery and scanning techniques are designed to assess configuration, traffic patterns, and security posture without extracting the content of your data. As an ISO 27001 certified organisation, we handle all audit data under strict controls.

What is the difference between a network audit and a penetration test?

A network audit is a broad assessment of performance, design, security, and compliance across your whole estate. A penetration test is a focused, adversarial exercise that actively attempts to exploit specific vulnerabilities. The two are complementary, and an audit often identifies where a penetration test would add value.

What size of business do you work with?

We audit everything from single-site offices to large, multi-site enterprises and hybrid cloud estates. Our methodology scales to the environment, and the scope is always tailored to your size and complexity.

We already have network monitoring. Do we still need an audit?

Monitoring tells you how your network is behaving now. An audit tells you whether it is designed, configured, secured, and documented correctly, and where the hidden risks sit. The two answer different questions, and most monitored networks still benefit from an independent audit.

Which standards and frameworks do you audit against?

We align audits with the frameworks relevant to your business, including ISO 27001, Cyber Essentials and Cyber Essentials Plus, PCI DSS, UK GDPR, and FCA operational resilience. If you have a specific compliance obligation, we build it into the scope.

Can a network audit help us meet Cyber Essentials, PCI DSS, or other standards?

Yes. An audit identifies where your network already meets a given standard and where the gaps are, covering controls such as firewall configuration, network segmentation, patching, and access management. It does not issue the certification itself, but it gives you a clear, prioritised path to readiness, which makes formal assessment faster and less costly.

What happens after the audit? Are we locked in?

You receive a prioritised remediation plan that any competent IT team can act on. If you would like us to carry out the work, our engineers can remediate and improve the network, but there is no obligation. The report is yours to use as you see fit.

How soon can you start?

Following a discovery call to agree scope, we can typically begin discovery within days. For urgent situations, our Rapid Engineer Deployment Team can mobilise quickly.