Information Security at Opticore

Protecting what matters to our business, our clients and our partners

Our Approach to Information Security

As a modern, forward-looking business, Opticore recognises the importance of ensuring our operations run smoothly and without interruption, for the benefit of our customers, our people and the wider organisations we work with. To support this, we operate a formal Information Security Management System (ISMS), aligned with the international standard for information security, ISO/IEC 27001. This gives us a structured, business-driven framework for identifying risks and implementing the right controls to manage them, rather than a one-off or reactive approach to security.
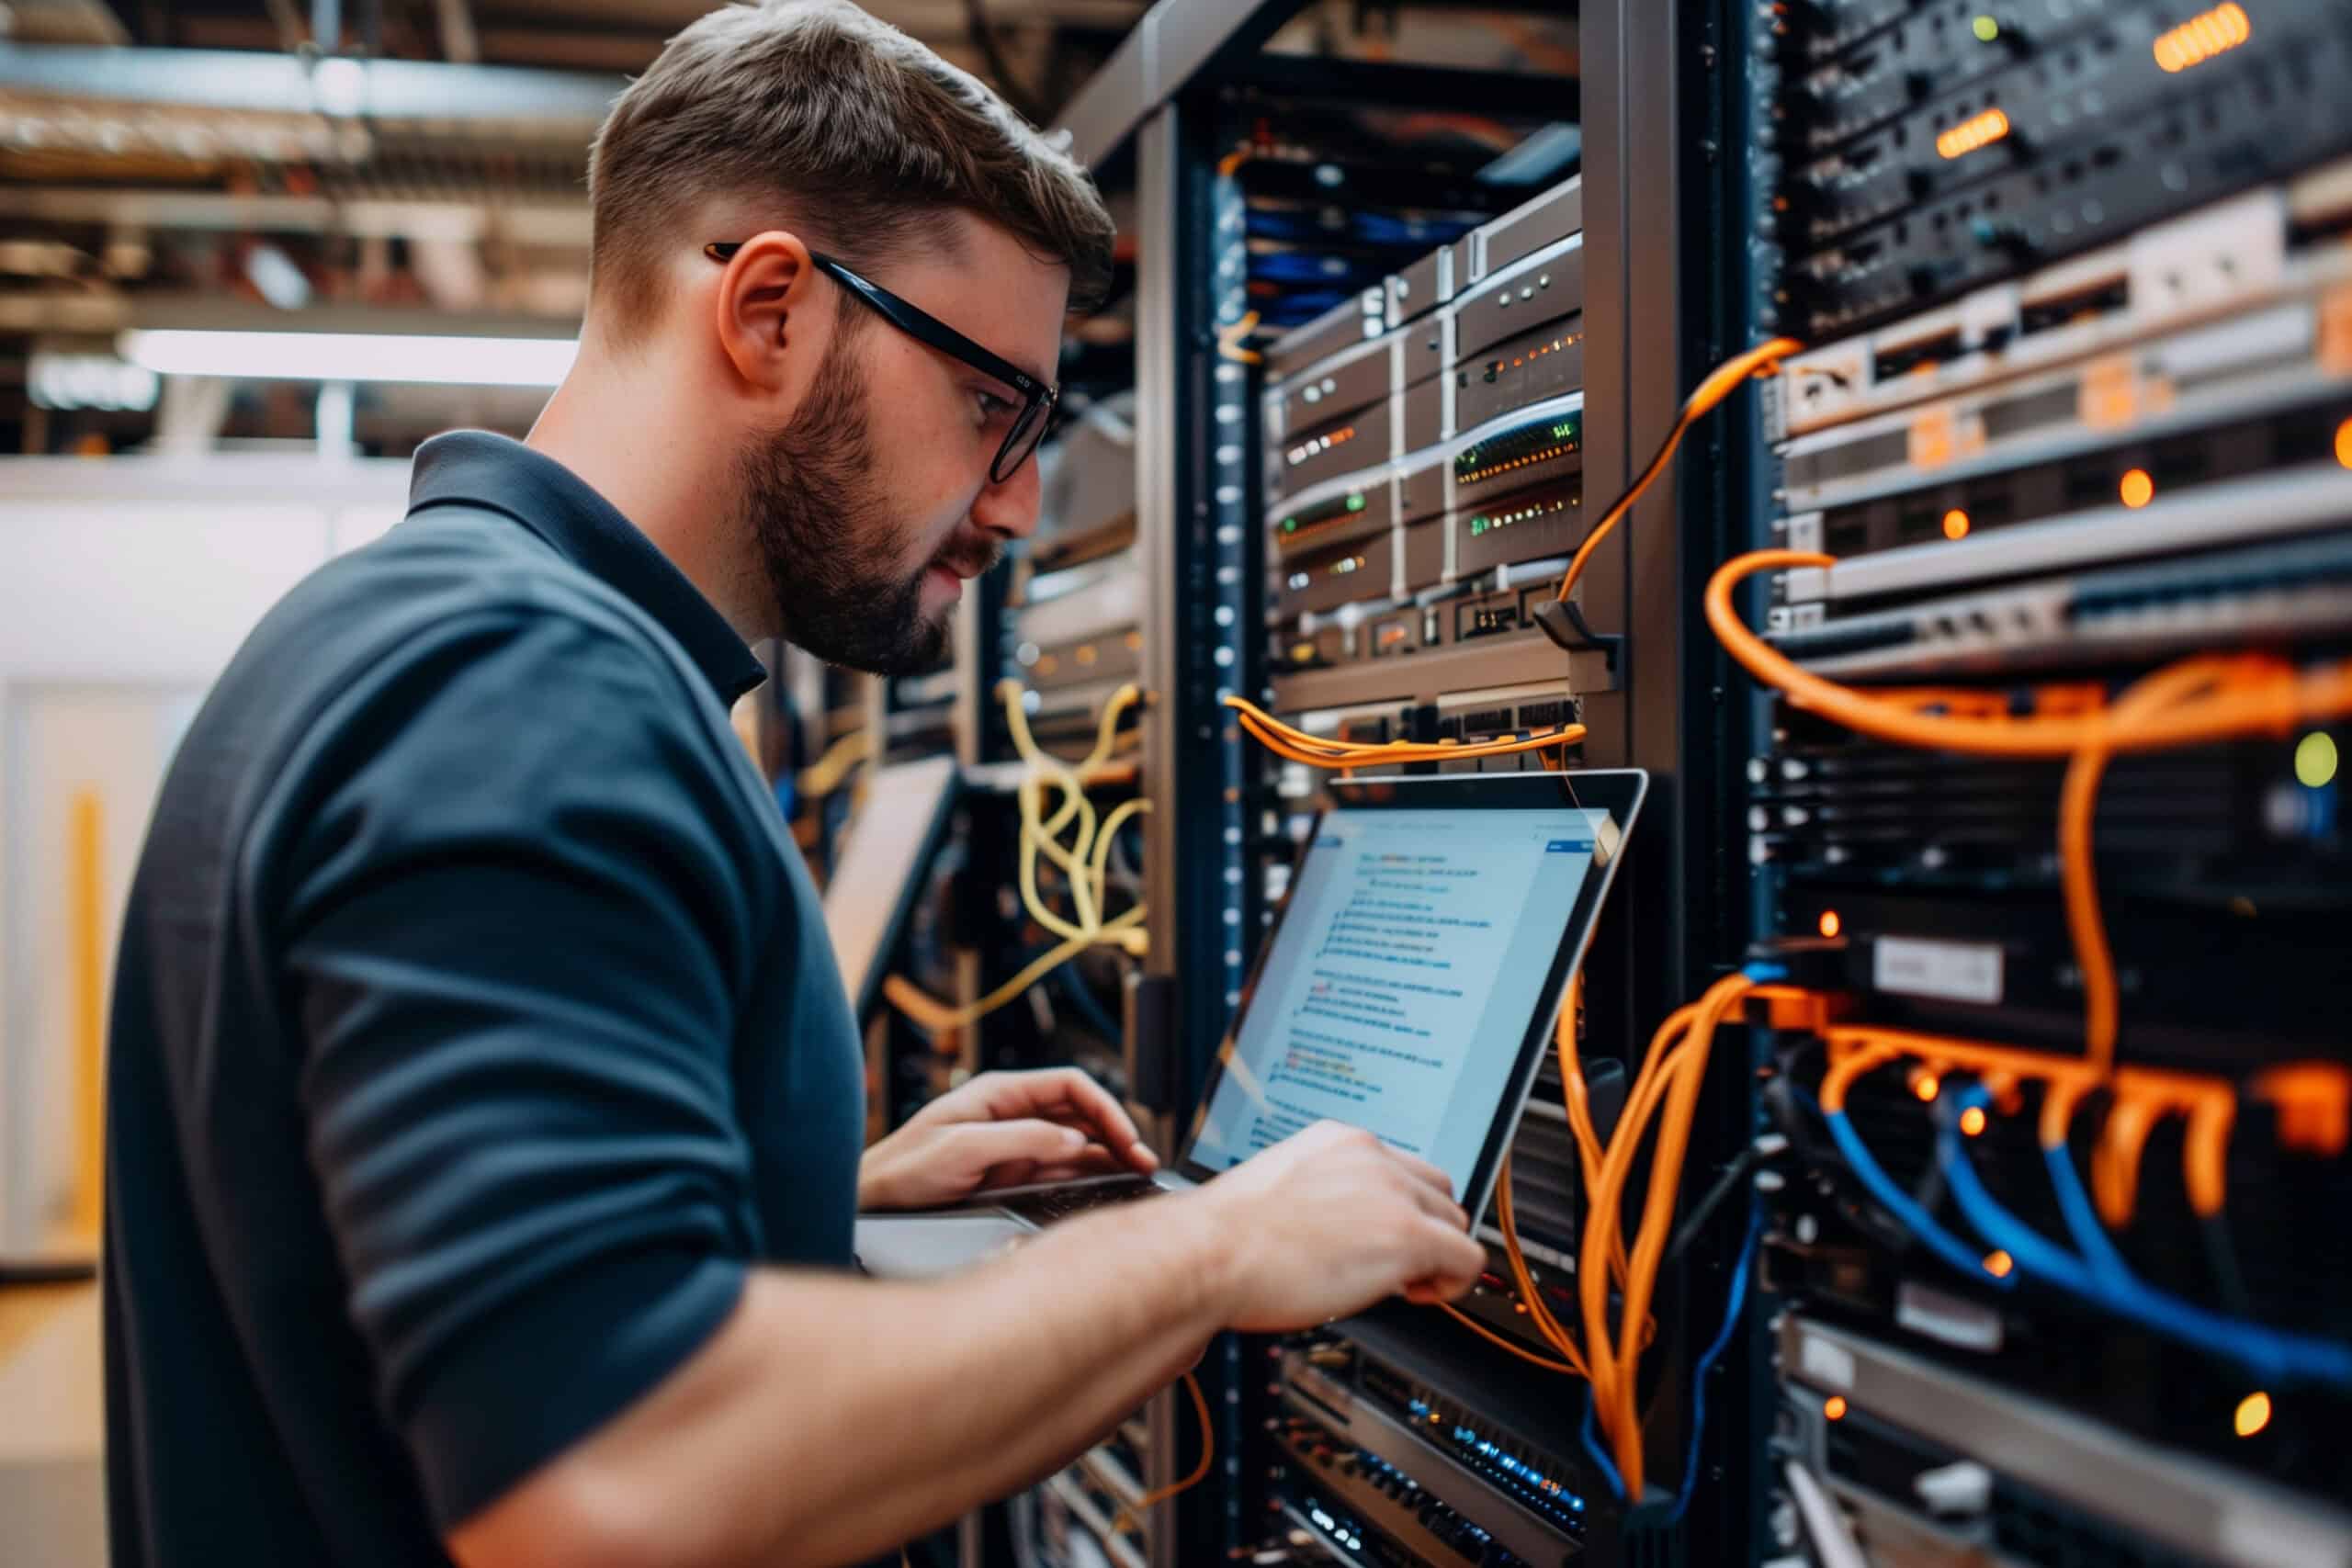
Server technician working on network cables and servers in data center.

Why Information Security Matter To Us

Our approach to information security delivers benefits across the business and for the people we work with, including:

– Protecting the continuity and reliability of the services we deliver
– Safeguarding company information, along with information belonging to our clients and suppliers
– Meeting our legal, regulatory and contractual obligations
– Supporting long-term trust and confidence with our customers, shareholders and partners

Information security requirements are agreed and maintained in line with business needs, and are regularly communicated to our people through team meetings and briefings, so that security remains embedded in how we work day to day, not treated as a separate function.

High-tech cryptocurrency mining rig with multiple graphics cards and blue USB connections.

A Framework for Continual Improvement

We don’t treat information security as a fixed state. Objectives are set on a regular cycle, informed by risk assessments and reviewed through management oversight, so that our controls stay relevant as the business, our clients’ needs and the threat landscape evolve.

This includes maintaining our certification to ISO/IEC 27001 on an ongoing basis, independently audited by a Registered Certification Body, and drawing on wider recognised codes of practice such as ISO/IEC 27002 to strengthen our controls further.

Ideas for improvement can come from anywhere, our own people, our clients, our suppliers, or the outcomes of risk assessments and service reviews, and are formally considered as part of our management review process.

A Comprehensive Set of Policies

Our overarching Information Security Policy is supported by a wide range of detailed policies covering areas such as access control, data protection, supplier security, business continuity, secure development and acceptable use, among others. Each is owned by someone with relevant competence, formally approved by senior management, and reviewed regularly to stay current.
office meeting

What This Means for You

Whether we’re delivering consultancy, managing your network, or supporting your cloud transformation, you can be confident that:

– Your information is handled with care and protected using industry-recognised best practice
– Risks are actively identified, assessed and managed, not just documented
– Our approach is governed by a formal management system, and independently verified through ISO/IEC 27001 certification
– Security is a standing commitment from our senior leadership, not an afterthought

Further detail on our certification, including scope, is available on request.